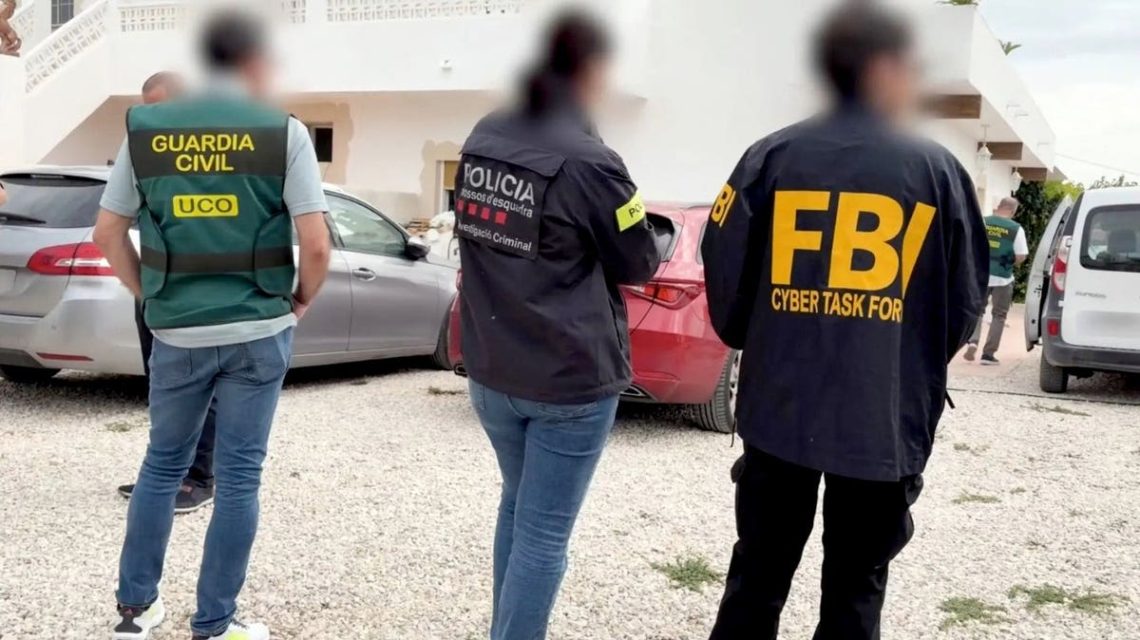
Imagine a 16-year-old leading a global ransomware group. Investigators have linked a teenager to KillSec, responsible for around 1,000 cyberattacks. About 500 attacks have been successful.
Authorities have now taken KillSec’s leak site and servers offline. They secured 110 terabytes of stolen data. This action highlights how accessible cybercrime has become.
Operation KillSwitch Stops KillSec
On September 30, authorities executed Operation KillSwitch. Police from the United States and Europe joined forces. Organizations like Europol and Eurojust coordinated efforts.
Police conducted searches in Greece, Romania, Spain, and the UK. They seized five servers tied to KillSec’s operations, including a dark web leak site.
Teen at the Helm of Cybercrime
The case reveals a 16-year-old as the suspected leader of KillSec. Another member, recently 18, was involved while still a minor. Investigators also identified roles such as negotiator and affiliate.
KillSec exploited software flaws and unsecured access points. They copied sensitive data and threatened to publish it unless victims paid.
AI’s Role in Ransomware
Europol reported that KillSec used artificial intelligence. AI helped in building infrastructure and selecting victims. This illustrates how cybercriminals employ familiar technology to enhance efficiency.
Ongoing KillSec Investigation
Authorities continue to analyze seized evidence. They are tracking cryptocurrencies and potential criminal proceeds. The number of confirmed attacks might rise as investigations progress.
Ransomware groups often reorganize under new names. Prevention remains crucial even after significant takeovers.
Lessons from KillSec Takedown
Though KillSec mainly targeted organizations, everyone can learn from their methods. They exploited vulnerabilities and weak access points.
Here are seven security practices to reduce ransomware risks:
- Install software and security updates. Keep systems current to fix known vulnerabilities.
- Use strong, unique passwords for each account. Password managers can help.
- Enable two-factor authentication on crucial accounts.
- Maintain offline backups of essential files, separate from compromised devices.
- Be cautious with unexpected downloads and attachments.
- Install security software on all devices.
- Know what to do if ransomware strikes. Disconnect affected devices from networks.
These steps can increase your security significantly.
The KillSec case draws attention due to the age of its suspected leader. Yet, the methods used are familiar. Vulnerable software and weak protections still provide criminals access.
Focus on basics. Update your devices, secure accounts beyond passwords, and keep unreachable backups. These actions can be crucial.
 Concerns Raised Over Safety of ChatGPT for Teens
 OpenAI Firings Spark Concerns Over AI Safety Discourse
 OpenAI Uncovers Russian and Iranian Influence Operations Using AI
 U.S. Restricts Microsoft on Foreign Worker Employment
 How iOS, Samsung, and Pixel Phones Tackle Scams and Protect Users
 A Comprehensive Guide to Choosing Husqvarna Chain Saws