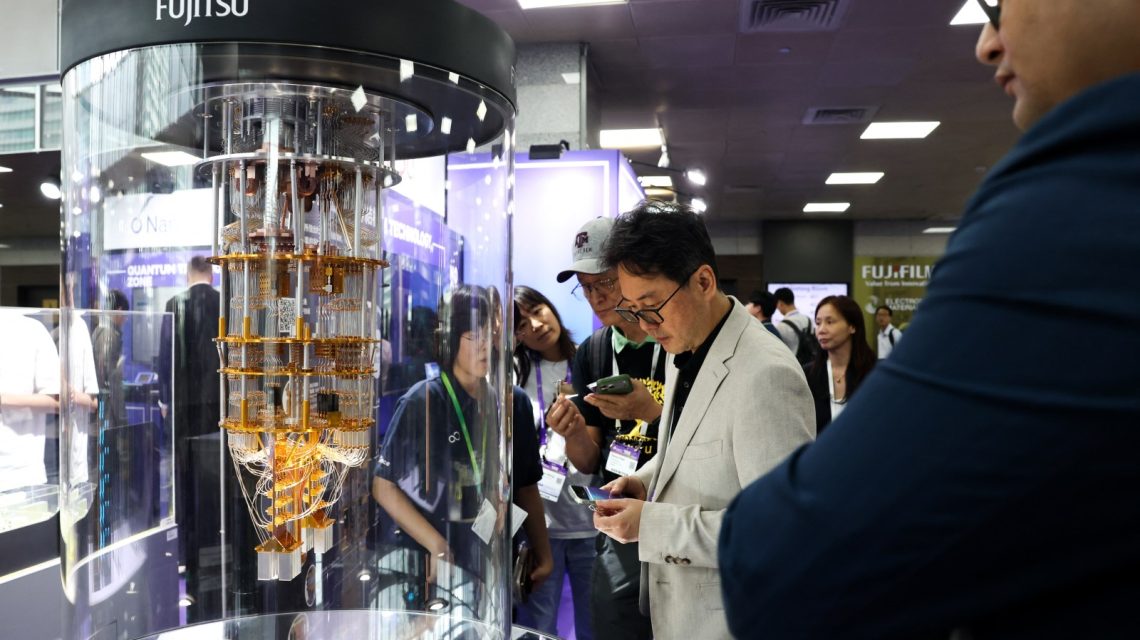
Quantum security has shifted from a distant technical concept to an essential infrastructure challenge. Companies once treated quantum risk as an abstract concern that they might address in the future. Today, that stance is increasingly difficult to justify.
Financial institutions, cloud providers, and digital asset platforms depend on cryptography to guard assets, identities, communications, approvals, and transactions. If cryptographic foundations must change, the transition will be intricate, lengthy, and sensitive. Starting early makes practical sense.
Why Quantum Computing Risks Are Significant
Quantum computing poses a straightforward threat. Quantum computers might eventually compromise many public-key cryptographic systems that secure digital signatures, encrypted communications, identity systems, and financial transactions. Organizations with high-value assets must prepare by adopting quantum-safe encryption techniques, which is a complex process.
The journey to quantum security is fraught with uncertainty. Companies are urged to prepare for quantum threats before a definitive quantum-safe infrastructure exists. While standards are emerging, many questions about implementation remain unanswered. This uncertainty can tempt executives to delay action, which would be a serious mistake.
Early Adoption as a Competitive Edge
Investing in quantum security early gives companies an advantage in navigating one of the most challenging infrastructure transitions of the next decade. Early experimentation allows organizations to understand cryptographic dependencies, test architectures, build expertise, and avoid rushed decisions.
Understanding Cryptographic Dependencies
Many large firms lack a comprehensive understanding of their cryptographic infrastructure, which undermines efforts to secure systems from quantum threats. Identifying signature schemes, encryption systems, key management flows, authentication systems, vendor dependencies, cloud services, custody infrastructure, internal tools, and legacy systems is crucial.
Starting early enables companies to discern which systems rely on algorithms that could become vulnerable. Institutions must prioritize urgent tasks over low-risk systems instead of approaching quantum migration as a massive, uniform project. Early movers know what to fix, while latecomers may struggle to even know where to begin.
The Role of Early Testing
The U.S. National Institute of Standards and Technology (NIST) plays a pivotal role by evaluating and standardizing post-quantum cryptographic algorithms, which remain secure against future quantum computers. NIST’s work is an important milestone, but institutions must understand how quantum-safe signatures and encryption function within actual systems.
Institutions should test these systems against critical operational constraints. Questions about transaction size, latency, cost, approval workflows, key management, custody models, auditability, and resilience require careful consideration, especially for institutions using distributed signing and MPC-based custody.
Gradual Migration Reduces Pressure
Security migrations are not simple updates; they demand testing, audits, compatibility checks, vendor coordination, customer communication, governance approvals, and sometimes infrastructure changes. Starting early allows for pilots, hybrid architecture testing, performance evaluations, and phased upgrades.
Running classical and post-quantum systems in parallel initially can help test new protections without losing existing infrastructure that secures critical systems. Gradual migration enables careful decisions under manageable pressure.
Customer and Partner Expectations
Security is increasingly central to commercial due diligence. Enterprises, financial institutions, custodians, exchanges, wallet providers, and infrastructure partners must demonstrate how they manage operational risk. Customers and partners will inquire about quantum readiness as they assess systems essential to identity, transaction approval, communications, custody, and data protection.
Defining Market Standards
Early adopters often influence how stakeholders define acceptable practices. Companies experimenting with quantum-safe security now may help set migration timelines, hybrid deployment models, custody and signing architecture, risk governance, and vendor requirements. Early movers have a voice in defining responsible preparation.
Examples of Early Adoption
Leading financial institutions and technology companies are testing quantum-safe infrastructure in real, high-value scenarios. HSBC trialed quantum-secure technology for tokenized physical gold trading. JPMorgan Chase is developing quantum-safe digital signature capabilities for various financial applications. Google integrates post-quantum features into core infrastructure and recently announced quantum-safe digital signatures in Google Cloud.
These initiatives are preliminary but demonstrate a shift from treating quantum security as a theoretical problem. Institutions are testing, learning, and readying for a transition that will take years. Quantum readiness demands sustained preparation, practical testing, and a clear understanding of how cryptography supports modern infrastructure. The migration has begun; the question is which institutions will be prepared as it accelerates.
Jay Prakash is the founder and CEO of Silence Laboratories, an organization dedicated to developing quantum-safe infrastructure for institutions.
 Bill Gates Advocates for AI Regulation to Prevent Catastrophe
 Rising Optimism Amid Box Office Success and YouTube Influences
 AI’s Expanding Role in Everyday Life
 OpenAI’s AI Agents and the Growing Call for Regulation
 FAA Investigates Software Issue in Boeing 737 Max
 Senator Ted Cruz on America’s AI Race Against China