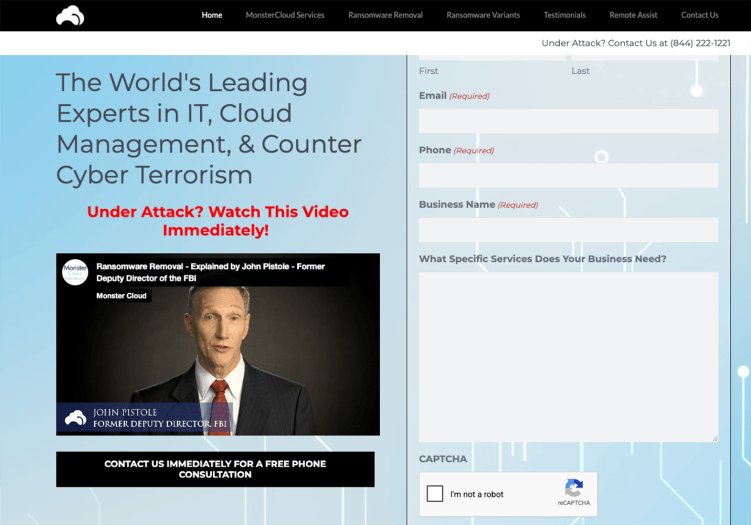
A Florida man, Zohar Pinhasi, was recently indicted on federal charges for defrauding clients of his ransomware data recovery business. The Justice Department alleges Pinhasi promised clients he could retrieve their encrypted files without paying hackers. In reality, he paid the ransom but charged clients extra fees.
The indictment confirms findings from a 2019 ProPublica investigation titled “The Trade Secret.” ProPublica discovered that victims of ransomware were victimized twice: by hackers and by MonsterCloud, Pinhasi’s data recovery firm. MonsterCloud misled clients, claiming they did not pay ransoms.
“By falsely claiming to decrypt ransomware without paying off the ransomers, the defendant re-victimized his clients while extracting a hefty profit for himself,” said U.S. Attorney Joseph Nocella in an October 7 press release. “Our Office will vigorously prosecute ransomware attackers who prey on Americans from across the world and those who cynically profit from their criminal activity.”
When ProPublica published its story, ransomware was a rising cyberthreat affecting governments, schools, and businesses. Hackers demanded ransom payments in cryptocurrencies. ProPublica’s reporting highlighted how industries like MonsterCloud and insurance firms fueled this extortion economy.
The threat continues, with hackers allegedly linked to foreign governments using ransomware for espionage. AI tools have made spreading ransomware easier.
Pinhasi, also known as Zack Green, told ProPublica that MonsterCloud did not promise clients data recovery through specific methods. He described the firm’s processes as a “trade secret.” This month, Pinhasi did not respond to inquiries from ProPublica.
A U.S. Attorney’s Office spokesperson said Pinhasi pleaded not guilty to the charges. ProPublica’s 2019 investigation involved interviews with MonsterCloud’s clients and experts, discovering that the firm sometimes paid ransoms for clients. MonsterCloud’s services appealed to law enforcement agencies who opposed paying hackers themselves. These agencies chose MonsterCloud based on the belief it did not pay ransoms.
Pinhasi claimed to be a former IT security officer for the Israeli military. He stated in 2019 that MonsterCloud handled up to 30 calls a day, with around 20 employees in South Florida. Federal investigators reported Pinhasi charged clients over $19 million and paid over $8 million in ransom payments. In one case, he paid about $8,200 but charged the client $150,000. If convicted, he faces up to 20 years in prison.
An FBI official remarked, “Pinhasi turned the victim’s crisis into his own profit center. This deception is unacceptable, and the FBI is committed to ensuring accountability for those who choose to victimize the very people who trusted them for help.”
The Justice Department did not comment on ProPublica’s 2019 revelation that John Pistole, a former FBI deputy director, was associated with MonsterCloud. Pistole appeared in a promotional video, endorsing MonsterCloud’s services. He stated that in most instances, data decryption involved paying hackers.
 Talcott Financial Group’s Retail Expansion and Technological Innovation
 Toyota’s Digital Transformation in Supply Chain Management
 Australia’s Challenge in Enforcing Social Media Restrictions for Minors
 State Attorneys General Grapple with Regulating Social Media Filters for Minors
 Innovative App Project Engages Students in Tree Assessment and GIS